Auth: API keys, JWT, and OAuth2
Auth: API keys, JWT, and OAuth2
Every authenticated route in Relay asks the same question: who is calling, and are they allowed? In FastAPI that question is a dependency. get_current_user reads a credential from the request, checks it, and returns a CurrentUser or raises a 401. Routes declare user: UserDep and never see the credential. What changes between schemes is only the first step: where the credential comes from and how it is verified.
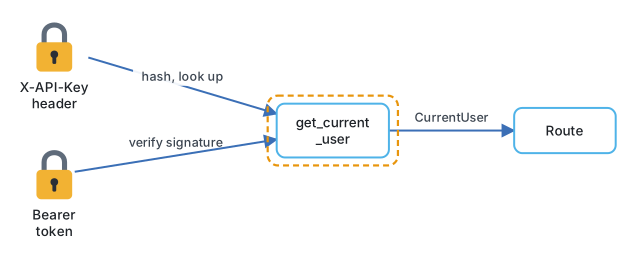
Relay needs two schemes. Machine clients (a customer's own backend calling /chat) send an API key in a header. People using the web client sign in once and then send a short-lived token. The fastapi.security module has a helper for each that also teaches /docs how to send the credential, so the Authorize button works.
Continue reading
Pro unlocks every video lesson, the full notes and runnable code across the Python with AI course, from the language itself to agents, MCP, Langfuse and deployment.